Buy kwzv.com ?
We are moving the project
kwzv.com .
Are you interested in purchasing the domain
kwzv.com ?
domain@kv-gmbh.de · 0541-91531010
Buy kwzv.com ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **

Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
All Categories Goods Portable Heavy Duty Ladder, Anti Slip Pedal, Safety Locking Design, Soft Handgrip, Compact And Durable Portable Heavy Duty Ladder, Anti Slip Pedal, Safety Locking Design, Soft Handgrip, Compact And DurableIntroducing the Heavy Duty Ladder that combines durability, safety, and portability in one essential tool. Whether you're tackling home improvement projects, accessing hardtoreach areas, or working outdoors, this ladder is designed to meet your...113,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Perfect Picks Market Foldable Leakproof Water Bottle For Kids And Sports Portable, Durable, And Compact For Basketball, Football, Tennis Foldable Leakproof Water Bottle For Kids And Sports Portable, Durable, And Compact For Basketball, Football, TennisStay hydrated wherever you go with the Foldable Leakproof Water Bottle. Perfect for sports enthusiasts, students, and anyone on the move, this portable water bottle easily fits into your bag or sports gear. Designed for kids and adults alike, its...35,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplifted Finds CARSUN Rechargeable Portable Tire Inflator CARSUN Rechargeable Portable Tire InflatorOptimize your roadside preparedness with the CARSUN Rechargeable Air Pump, a specialized industrial utility designed to act as an efficient solution for ondemand tire maintenance. Specifically engineered with a highperformance cordless framework and...237,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplifted Trends Foldable Silicone Travel Cup With Lid Compact Portable & Durable Water Cup For Camping Travel & Outdoors pinkWhether youre heading on a camping trip, hiking adventure, or a quick getaway, this foldable silicone travel cup 180 ML is the perfect companion. Crafted from durable, highquality silicone, it collapses for easy storage and includes a secure lid to...34,97 $*Shipping: 0,00 $Secure redirect to the provider


-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **

How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
All Categories Goods Scissor Jack Portable Lift Stand For ATVs, Motorcycles & Bikes Compact & Durable Scissor Jack Portable Lift Stand For ATVs, Motorcycles & Bikes Compact & DurableElevate your lifting game with this scissor jack stand designed for ATVs, motorcycles, and bikes. Perfect for home garages or professional mechanics, this portable tool provides the convenience and strength you need to safely lift your vehicle. With...149,97 $*Shipping: 0,00 $Secure redirect to the provider
-
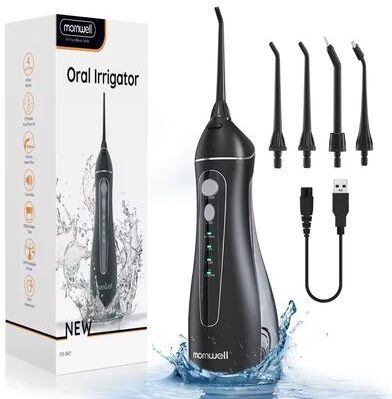
Uplift Essentials Portable Cordless F18 Oral Irrigator 3 Modes, Waterproof, Rechargeable, 4 Nozzles Portable Cordless F18 Oral Irrigator 3 Modes, Waterproof, Rechargeable, 4 NozzlesPortable Cordless F18 Oral Irrigator 3 Modes, Waterproof, Rechargeable, 4 Nozzles Elevate your oral hygiene routine with the Portable Cordless F18 Oral Irrigator, designed to provide a deep and thorough clean. This compact device offers three...132,45 $*Shipping: 0,00 $Secure redirect to the provider
-
All Categories Goods Portable Heavy Duty Ladder, Anti Slip Pedal, Safety Locking Design, Soft Handgrip, Compact And Durable Portable Heavy Duty Ladder, Anti Slip Pedal, Safety Locking Design, Soft Handgrip, Compact And DurableIntroducing the Heavy Duty Ladder that combines durability, safety, and portability in one essential tool. Whether you're tackling home improvement projects, accessing hardtoreach areas, or working outdoors, this ladder is designed to meet your...113,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Perfect Picks Market Foldable Leakproof Water Bottle For Kids And Sports Portable, Durable, And Compact For Basketball, Football, Tennis Foldable Leakproof Water Bottle For Kids And Sports Portable, Durable, And Compact For Basketball, Football, TennisStay hydrated wherever you go with the Foldable Leakproof Water Bottle. Perfect for sports enthusiasts, students, and anyone on the move, this portable water bottle easily fits into your bag or sports gear. Designed for kids and adults alike, its...35,97 $*Shipping: 0,00 $Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for Tpm
-
Uplifted Finds CARSUN Rechargeable Portable Tire Inflator CARSUN Rechargeable Portable Tire InflatorOptimize your roadside preparedness with the CARSUN Rechargeable Air Pump, a specialized industrial utility designed to act as an efficient solution for ondemand tire maintenance. Specifically engineered with a highperformance cordless framework and...237,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplifted Trends Foldable Silicone Travel Cup With Lid Compact Portable & Durable Water Cup For Camping Travel & Outdoors pinkWhether youre heading on a camping trip, hiking adventure, or a quick getaway, this foldable silicone travel cup 180 ML is the perfect companion. Crafted from durable, highquality silicone, it collapses for easy storage and includes a secure lid to...34,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplifted Trends Foldable Silicone Travel Cup With Lid Compact Portable & Durable Water Cup For Camping Travel & Outdoors greenWhether youre heading on a camping trip, hiking adventure, or a quick getaway, this foldable silicone travel cup 180 ML is the perfect companion. Crafted from durable, highquality silicone, it collapses for easy storage and includes a secure lid to...34,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Uplifted Trends Foldable Silicone Travel Cup With Lid Compact Portable & Durable Water Cup For Camping Travel & Outdoors yellowWhether youre heading on a camping trip, hiking adventure, or a quick getaway, this foldable silicone travel cup 180 ML is the perfect companion. Crafted from durable, highquality silicone, it collapses for easy storage and includes a secure lid to...34,97 $*Shipping: 0,00 $Secure redirect to the provider
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.